Passguard launches ClickFix Observer: track ClickFix attacks for free
ClickFix Observer is a free public dashboard that tracks ClickFix attacks as they happen, with more than 9,000 confirmed lures at launch.
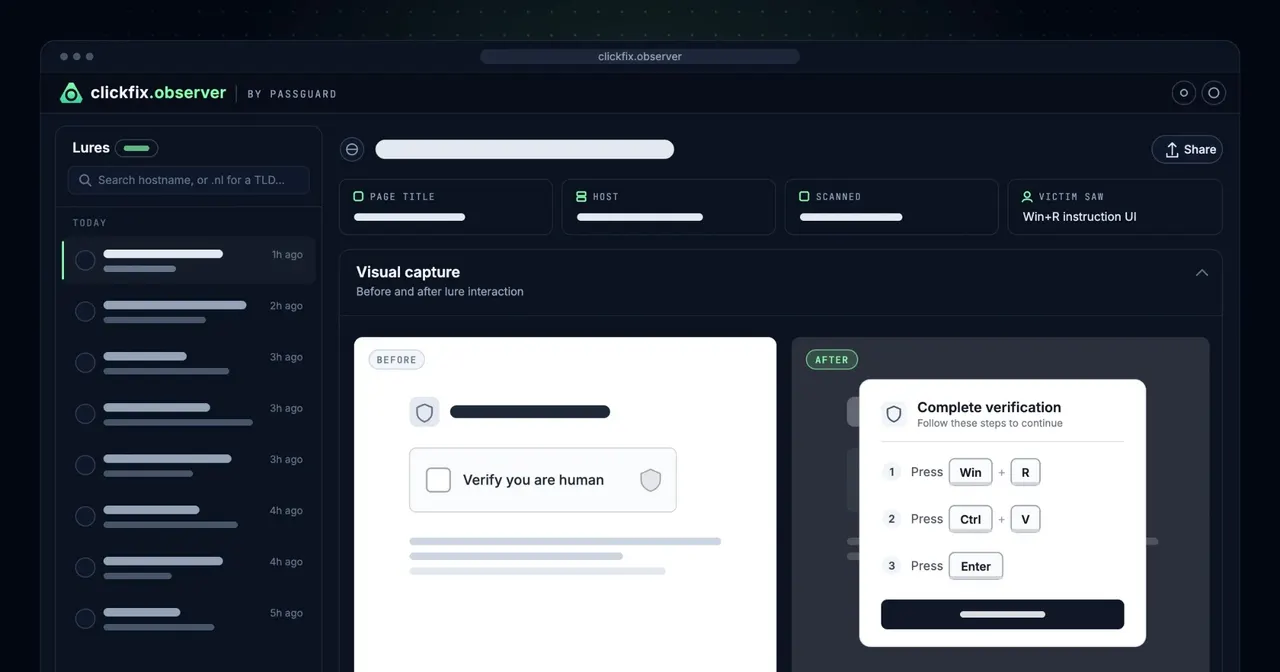
Today we're launching ClickFix Observer, a free public dashboard at clickfix.observer that shows ClickFix attacks as they happen on the web. At launch it holds more than 9,000 confirmed lures, and the number grows every hour.
Why we built it
Passguard monitors criminal marketplaces to detect infostealer infections before attackers can exploit them. Every day we see stolen credentials and session tokens appear for sale. For most of our customers, that is the first moment they learn a device was infected.
By then the interesting part is already over. When we traced stolen data back to its source, we increasingly landed on the same thing: a compromised WordPress site showing a fake CAPTCHA.
That technique is called ClickFix, and it's growing fast. ESET's latest threat report shows ClickFix detections grew by 108% between H2 2025 and H1 2026 (ESET Threat Report H1 2026). So we did what we already do for criminal marketplaces: we built automated collection.
What is ClickFix?
ClickFix is a social engineering technique that gets people to infect themselves. Instead of asking you to download and open a file (which antivirus is good at catching), it asks you to paste and run a command.
The lure usually looks like a "verify you are human" checkbox, a fake error message or a Cloudflare-style prompt. Click through and this happens:
- A malicious PowerShell command is silently copied to your clipboard.
- A short set of instructions tells you to press Win+R, then Ctrl+V, then Enter.
- The command runs with your permissions and fetches the real payload, usually an infostealer such as Lumma Stealer.
Nothing is downloaded through the browser. The command never appears in the address bar, only in the Windows Run dialog. And you typed the keystrokes yourself.
What ClickFix Observer shows
Every entry is a confirmed lure, not a page that merely looks suspicious. We only list a site when our scanners have captured the technique in action in a real browser: the command placed on the clipboard and the paste-and-run instructions shown to the visitor.
For each lure you get:
- Before and after screenshots: the page before and after the fake CAPTCHA is clicked
- The extracted payload: the exact clipboard command, defanged, with its download URL
- The attack chain: from lure site to delivery host to payload, step by step
- Infrastructure: the compromised domain, the host serving the kit and its IP address, ready to use as indicators of compromise
Who it's for
ClickFix Observer is built for SOC and threat intelligence teams, incident responders, researchers, site owners and security awareness teams.
ClickFix lures sit on ordinary compromised websites and catch anyone who visits, regardless of industry, so we've made the data public.
Start observing
ClickFix Observer is live at clickfix.observer. It's free, and you don't need an account to browse the feed or open a report.
If you find your own domain in the list, treat it as a confirmed compromise and remove the injected scripts. Want to know whether your organisation is already affected? Start a free scan.
We'll keep watching. Now you can too.
See it yourself
See what infostealers already stole from your organisation.
Free · No signup · Results in about a minute